A single nearby attacker could listen through unpaired Beats Studio Buds under the right conditions, while cloud connectors, Android TV boxes, and airline recovery systems exposed the same lesson: security risk is clustering in tools people don't audit hard enough.
XOOMAR Intelligence
Analyst Take
This cybersecurity news roundup centers on incidents that didn't all dominate the week, but should worry product teams, cloud operators, and anyone responsible for third-party technology risk. The details come from SecurityWeek, which pulled together updates spanning patched hardware flaws, cloud escalation paths, botnet infrastructure, long-running espionage, and post-outage accountability.
Device makers face the Beats warning: microphones are attack surfaces
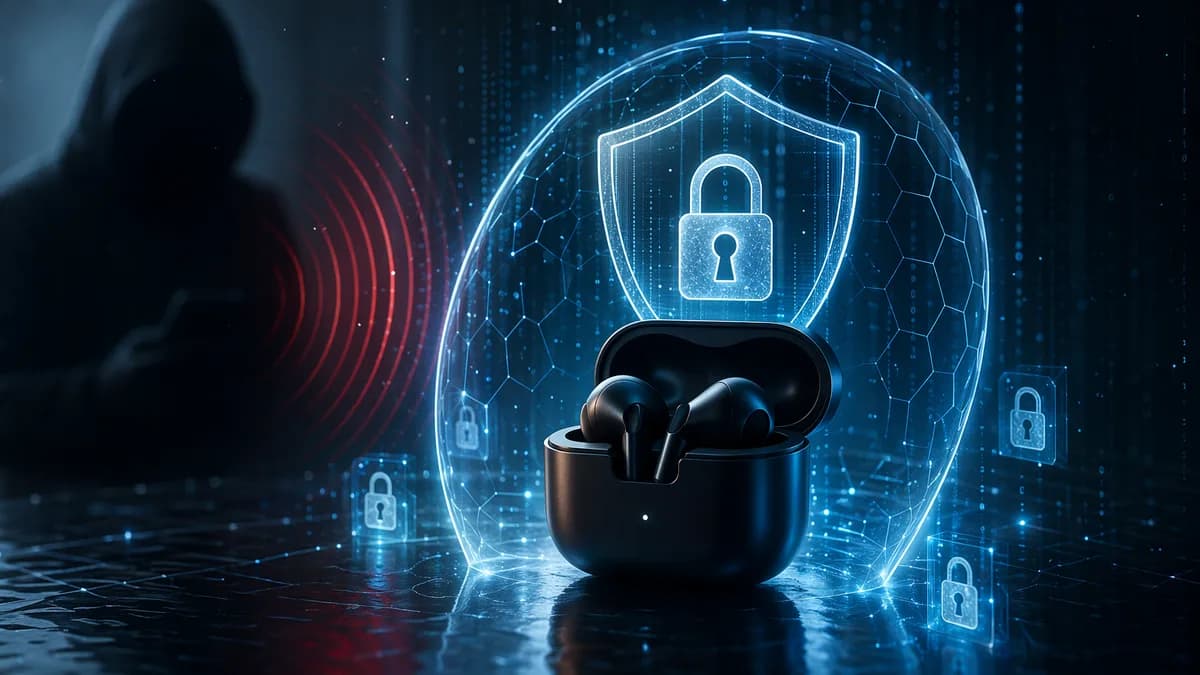
Apple released Beats Studio Buds firmware update 1B211 to patch CVE-2025-20701, a Bluetooth security issue that allowed nearby attackers to listen through the microphone on unpaired devices actively seeking connections. Ars Technica, citing Apple’s advisory, reported the flaw carried a severity rating of 8.8 out of 10.
“Impact: An attacker within Bluetooth range may be able to listen through the microphone of a device which is not yet paired and actively seeking pair requests,” Apple said.
Who should treat this as more than a headphone bug? Product security teams building anything with microphones, Bluetooth pairing, companion apps, or automatic firmware delivery.
The fix applies automatically when the earbuds are paired with Apple devices. That matters because accessories often sit below phones and laptops in users’ mental patch queue. The privacy risk is not theoretical in design terms: audio gear combines sensors, wireless proximity, and often opaque firmware update flows.
Readers tracking the specific hardware privacy angle can also see our related piece, Spies Could Listen Through Patched Beats Studio Buds Flaw.
Airlines get a regulatory signal from Delta’s CrowdStrike closure
The US Department of Transportation closed its investigation into Delta’s 2024 CrowdStrike outage response without penalties. SecurityWeek said investigators found the airline provided adequate refunds, baggage help, and support for passengers with disabilities.
For airlines and other consumer-facing operators, the question is blunt: can they recover fast enough when a vendor failure cascades into the customer experience?
The closure reduces one legal pressure point for Delta, but it doesn't erase the operational lesson. A software incident tied to a third-party provider can still become a brand, logistics, and passenger-support crisis. Regulators stepping back in this case doesn't mean the resilience bar drops. It means airlines have to prove their recovery plans work before the next outage tests them in public.
Cloud teams get AWS Continuum, but automation still needs proof
AWS Continuum is a new AI-powered tool in gated preview that helps organizations discover, prioritize, validate, and resolve vulnerabilities. According to SecurityWeek, it pulls findings from existing tools and its own scanning, then prioritizes them based on exploitability in the customer’s own environment.
That framing fits the pressure cloud teams face: too many alerts, too many services, and not enough confidence that the riskiest issue is actually first in line.
The useful question for builders is not whether Continuum sounds promising. It’s whether it integrates deeply enough with existing workflows, produces high-quality prioritization, and exposes the reasoning behind its findings. Customers should test data access, alert quality, validation logic, and cost before treating any security platform as a complete answer.
For teams thinking about how cloud tooling and test strategy shape operational risk, LocalStack vs Testcontainers Splits Cloud Test Strategy offers adjacent context.
Android TV buyers become part of the proxy problem
Researchers linked the large Popa Android TV box botnet to NetNut, a residential proxy provider operated by publicly traded Israeli company Alarum Technologies. SecurityWeek said the botnet was used for residential proxy traffic in ad fraud and scraping, with researchers saying an SDK turns compromised streaming devices into persistent proxies.
NetNut and Alarum disputed the allegations, calling them “demonstrably inaccurate assertions and flawed deductions rather than verified facts.”
That denial matters. Attribution involving commercial infrastructure is messier than a simple criminal or state-backed label, especially when proxy networks, SDKs, and consumer devices overlap.
For end users, the immediate question is narrower: what else is a cheap streaming box doing on the network? The source does not specify the initial compromise path. Still, the case puts pressure on buyers and IT teams to scrutinize firmware updates, app sources, vendor support, and always-on devices that rarely get monitored after setup.
Enterprise defenders learn the Velvet Ant lesson: persistence beats noise
Velvet Ant, described as a China-nexus actor, reportedly compromised an organization’s segregated network starting around 2016. The group chained internet-facing footholds, Nginx/FastCGI proxies, and backdoored PAM/OpenSSH components for credential theft and persistent access.
SecurityWeek said the actor deployed variants of GS-Netcat, SOCKS5 proxies, and nine pam_unix.so backdoors across hosts. Remediation proved complex.
The hard question for defenders: if an attacker can stay for years, which alerts are getting ignored, suppressed, or never generated?
This was not a flashy smash-and-grab. The signal is patience. Long dwell time points to weaknesses in segmentation, credential hygiene, asset visibility, and detection coverage. It also shows why “air-gapped” or segregated environments still need active monitoring and disciplined remediation paths.
Kubernetes operators face a GCP Config Connector escalation path
A confused deputy vulnerability in GCP Config Connector can let any Kubernetes namespace user escalate to GCP Organization Owner by submitting a malicious IAMPolicyMember, according to SecurityWeek. Google acknowledged the issue internally as P1/S1, later classified it as “working as intended,” and left it unpatched.
That is a sharp finding because Config Connector exists to manage Google Cloud resources through Kubernetes-style declarations. If the controller has broad authority, a namespace-level mistake can become an organization-level problem.
Cloud security teams should ask one operational question: who can submit resource definitions that powerful controllers will honor?
Practical defenses follow from the reported issue:
- RBAC: Tighten who can create or modify relevant Kubernetes resources.
- Service accounts: Audit permissions tied to Config Connector.
- Namespace access: Limit who can operate in namespaces connected to cloud management.
- Monitoring: Watch Config Connector activity for IAM changes.
- Vendor guidance: Apply any future Google guidance or fixes when available.
The bigger picture: forgotten tools are becoming first-entry risks
This cybersecurity news roundup points to a common failure pattern. The risky systems are not always crown-jewel databases or high-profile apps. They are earbuds, TV boxes, cloud controllers, airline software dependencies, and stealthy footholds in supposedly separated networks.
Attackers benefit when organizations rank assets by visibility instead of consequence. A microphone accessory can become a privacy issue. A Kubernetes controller can become a cloud control-plane issue. A streaming device can become proxy infrastructure. A vendor outage can become a passenger crisis.
The practical takeaway is uncomfortable but useful: audit the tools that feel too ordinary to matter. Security teams already know these devices and services exist. The next major incident may start with the one they placed too low on the priority list.
Impact Analysis
- Apple patched a Beats Studio Buds flaw that could let a nearby attacker listen through an unpaired device’s microphone.
- The incident shows how Bluetooth accessories and opaque firmware update flows can create overlooked privacy risks.
- The broader roundup highlights growing security exposure in third-party tools, cloud connectors, and recovery systems.
Beats Studio Buds Vulnerability Severity
Primary Sources & Disclosures
Written by
XOOMAR
Data desk
XOOMAR is a capital markets software and data company. Every brief on this site starts from a dataset the company collects itself from primary sources (CFTC, SEC EDGAR, FINRA, the Federal Reserve, exchange APIs) and names the numbers it is built on, with a link to the data page so you can check them. Briefs are reviewed before they go out and corrected in place when the data is revised.